Most WordPress security happens in the wrong place.
The typical setup is a security plugin running on the website itself, which means every attack reaches your server before the plugin tries to stop it.
Your hosting resources get spent processing hostile traffic. Your site slows down under scanning floods, the thousands of automated requests a day from bots probing for a way in, each one your server has to stop and answer. And if the attacker finds a gap, they’re already inside the house.
Here’s what that costs you. That same flood is also slowing your site for the person who just landed on your homepage or is halfway through a checkout, and visitors don’t wait.
The attacker who slips past the plugin doesn’t announce it; the first sign is often a warning next to your business name in Google search, and getting that removed takes days of lost traffic and lost trust. And these bad days have a habit of arriving on a Saturday.
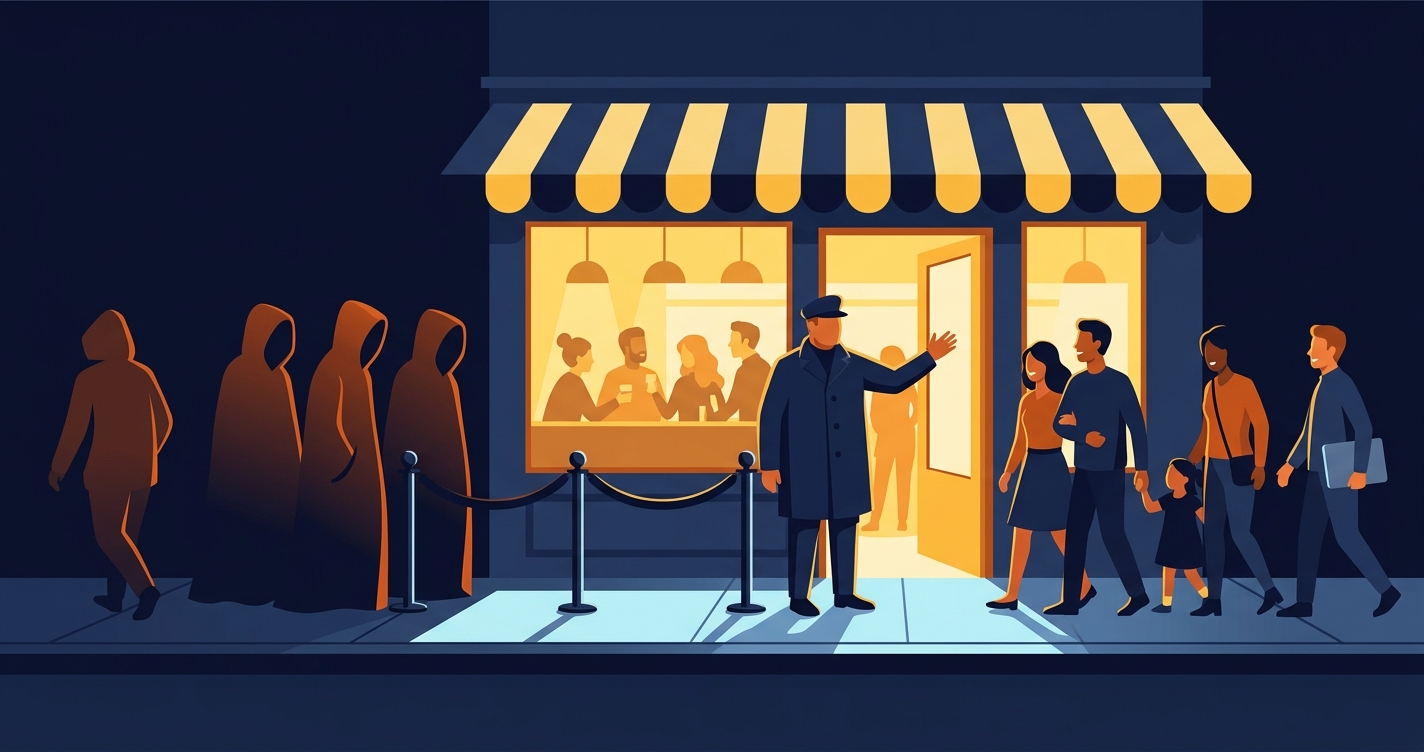
The better setup is an edge firewall: a filter that sits between the internet and your website and decides which requests are allowed to reach your server at all.
Think of it as a bouncer at the front door of the building, not a guard sitting inside your office. The guard inside only meets intruders who have already made it past the door.
That’s how we do it. Every site we manage sits behind Cloudflare’s global network, the same infrastructure protecting some of the largest companies on the internet. We’ve spent years refining a custom set of firewall rules that decide who gets in before a single request touches your server.
Cloudflare operates hundreds of datacenters around the world. When someone requests your website, that request hits the nearest Cloudflare datacenter first, and that’s where our rules do their work. That’s what “the edge” means: the outer boundary of the network, as far from your server as a request can be stopped.
The advantages compound:
Tired of dealing with this yourself? That's exactly what we handle.
See our plans →Aggressive blocking is easy. Blocking the right things without breaking the site is the hard part, and it’s where generic security settings quietly cost businesses money.
Cloudflare out of the box is good. Cloudflare tuned by people who manage WordPress fleets for a living is something else. Our rules, developed and refined across years of real attack traffic, work in layers:
Across the sites we manage, this filtering blocks or challenges more than 2 million hostile requests every month. Our clients’ visitors never see a security prompt they shouldn’t; our clients’ servers never waste a cycle on an attacker.
And the rules aren’t static. Attack patterns change constantly, so our ruleset evolves with them.
Every week, what’s actually hitting the fleet is analyzed and turned into proposed rule changes, which we review and push out to every site at once. When one site gets attacked, every site we manage gets the defense.
We also watch published threat research, so when a new WordPress attack technique is reported, it can be blocked at the edge before a patch even exists. (More on how we automated that intelligence in a companion post.)
Every one of those layers could break a real site if it were applied bluntly. That’s the part most providers get wrong.
Our rules are built with carefully maintained exceptions, so the things your site depends on keep working:
Security that breaks your business isn’t security. Getting that balance right is what our years of refinement are for.
We don’t take that balance on faith, either. Before any rule change goes live, it’s tested against weeks of real visitor traffic across every site we manage, and every match is sorted into “attacker” or “something legitimate that might get caught.” Nothing ships until that comes back clean.
And AI is handled by choice, not by accident: whether AI assistants and their crawlers can access your site is a decision we configure to your preference, keeping you visible in AI-powered search if you want to be, or protecting your content from training crawlers if you don’t.
If your site is under our management, all of this is already active: configured, monitored, and maintained as part of the service.
A standing check confirms your traffic is actually routing through the wall, because rules on a bypassed site protect nothing.
For our clients, that means no plugin to update, no settings to tune, no performance trade-off. We just take care of it.
If it isn’t, and your current security amounts to a plugin and hope, we’d be happy to take a look. No pressure, no commitment, just an honest read on what’s been knocking on your door and what’s getting through.
ONSiteWP has provided managed WordPress hosting with security built in since 2016: Cloudflare edge protection tuned by specialists, continuous vulnerability patching, and server-level malware scanning. Let’s talk about your site